LIVE FEED
Walmart Opens Platform to AI Shopping Agents With Spend Controls

Walmart Opens Platform to AI Shopping Agents With Spend Controls

FIRST LOOK ATLAS OWASP MEDIUM Moderate risk · Monitor closely ▲ 5.8 The Verge AI

Walmart is launching a structured AI agent access programme allowing third-party agents to shop on behalf of customers, complete with Agent Profiles, mandatory purchase approval workflows, and configurable spending limits. For defenders and platform security teams, this represents a meaningful early example of a retailer codifying agentic access governance — defining what agents may and may not do contractually and technically before widespread adoption normalises uncontrolled agent access. Residual gaps remain around agent identity verification, cross-platform behavioural monitoring, and the maturity of enforcement mechanisms when agents operate outside pre-approved parameters.

1Password Launches Agent Login Tool That Shields Credentials

1Password Launches Agent Login Tool That Shields Credentials

FIRST LOOK ATLAS OWASP LOW Limited impact · Standard review ▲ 7.2 TechCrunch AI

1Password has launched '1Password for Agents', a platform that allows AI agents to authenticate to web services on a user's behalf without ever receiving or storing the user's credentials, using a digital key exchange and real-time user confirmation flow. This closes a significant gap in agentic credential hygiene, where the current default is users manually handing plaintext passwords to agents — creating uncontrolled credential copies outside the user's management. Residual gaps remain around institutional adoption (notably financial services), ecosystem coverage across all agent platforms, and the absence of standardised agentic identity protocols that would extend this protection beyond 1Password's supported integrations.

OpenAI, Meta and Google AI Agents Blocked by Major Web Services

OpenAI, Meta and Google AI Agents Blocked by Major Web Services

FIRST LOOK ATLAS OWASP MEDIUM Moderate risk · Monitor closely ▲ 6.8 The Verge AI

Major financial institutions, airlines, and web platforms including JPMorgan Chase, Delta, and Yelp are actively blocking AI agents from OpenAI, Meta, Google, and others from accessing their services, citing security and licensing concerns. This organic emergence of access-control enforcement at the perimeter closes a meaningful gap by demonstrating that web services can assert identity-based boundaries against autonomous agents before harm occurs. Residual gaps remain around standardisation — there is no common agent-identity protocol, so enforcement is fragmented, inconsistently applied, and difficult to audit or verify across the ecosystem.

AWS Adds Native Access Controls for RAG via Amazon Quick and Bedrock

AWS Adds Native Access Controls for RAG via Amazon Quick and Bedrock

FIRST LOOK ATLAS OWASP MEDIUM Moderate risk · Monitor closely ▲ 6.2 AWS Machine Learning Blog

AWS has introduced integrated access control capabilities for Retrieval-Augmented Generation (RAG) pipelines, combining Amazon Quick and Amazon Bedrock to enforce document-level permissions during AI-driven retrieval. This closes a meaningful gap for defenders: RAG systems have historically treated retrieval as a flat, permissionless operation, meaning users could receive AI-synthesised responses derived from documents they would not normally be authorised to read. Residual maturity questions remain around how granular these controls are at the chunk or passage level, whether they support complex identity federation scenarios, and how access policy drift is monitored over time.

Anthropic Launches 3-Tier Cyber Verification Program for AI Access

Anthropic Launches 3-Tier Cyber Verification Program for AI Access

FIRST LOOK ATLAS OWASP LOW Limited impact · Standard review ▲ 7.2 SecurityWeek

Anthropic has unified its Cyber Verification Program (CVP) and Project Glasswing into a single three-tier access framework that gates its most capable AI models based on verified defender credentials. This closes a meaningful gap by ensuring that high-capability AI is preferentially available to vetted security practitioners rather than being uniformly accessible, reducing the risk of misuse while accelerating legitimate defensive research. The residual question is how rigorous and scalable the verification process will be in practice, and whether the tiering logic aligns with the operational tempo of real security teams.

Enterprise IAM Framework for AI Agents Closes Identity Governance Gap

Enterprise IAM Framework for AI Agents Closes Identity Governance Gap

FIRST LOOK ATLAS OWASP MEDIUM Moderate risk · Monitor closely ▲ 7.8 The Hacker News

A practical enterprise framework for applying Identity and Access Management principles to AI agents has been published, treating each agent as a non-human identity with scoped authorisation, defined ownership, and continuous monitoring. This closes a critical visibility gap where conventional IAM platforms describe access as configured but cannot observe what an autonomous agent actually executed once inside an application — the so-called intent-to-execution gap. Residual maturity questions remain around tooling integration, runtime telemetry completeness, and the organisational readiness required to assign human ownership to every deployed agent identity.

SOC 2 Framework Adapts to Cover AI Agent Identity Controls

SOC 2 Framework Adapts to Cover AI Agent Identity Controls

FIRST LOOK ATLAS OWASP MEDIUM Moderate risk · Monitor closely ▲ 7.2 BleepingComputer

A sponsored analysis by Token Security argues that SOC 2's Trust Services Criteria are hollowing out under AI agent adoption, as the framework's core assumptions about account ownership, log attribution, and access approval no longer hold when agents act autonomously under human identities. The piece closes a conceptual gap by surfacing exactly which SOC 2 controls (CC6.1–CC6.3) are most exposed, giving compliance and security teams a concrete starting point for remediation and audit scope expansion. Realising the full benefit requires auditors, certification bodies, and organisations to reach consensus on treating AI agents as a distinct identity class — maturity that does not yet exist uniformly across the industry.

CISOs Deploy AI Agent Governance Controls to Cut Privilege Risk

CISOs Deploy AI Agent Governance Controls to Cut Privilege Risk

FIRST LOOK ATLAS OWASP MEDIUM Moderate risk · Monitor closely ▲ 6.5 SecurityWeek

Security leaders are accelerating efforts to establish governance frameworks that constrain over-privileged AI agents while preserving their operational utility. This addresses a critical maturity gap in agentic AI deployment — the absence of standardised controls for scoping agent permissions, auditing autonomous actions, and enforcing least-privilege principles at the agent layer. Residual gaps remain around tooling standardisation, cross-vendor interoperability, and the absence of consistent runtime monitoring frameworks for multi-agent environments.

Workflow Identity Hijacking Targets Enterprise AI Data Access

Workflow Identity Hijacking Targets Enterprise AI Data Access

ATLAS OWASP HIGH Significant risk · Prioritise patching ▲ 7.5 Dark Reading

A newly documented attack technique called 'workflow identity hijacking' exploits unauthenticated entry points in enterprise environments to bypass standard security controls and seize control of organisational data. The attack leverages the trusted identity context of automated AI workflows to move laterally and exfiltrate sensitive information. This represents a significant threat to enterprises relying on AI-driven automation pipelines where identity boundaries are not rigorously enforced.

GhostJacking Attack Hijacks AI Agents via Security Alerts

GhostJacking Attack Hijacks AI Agents via Security Alerts

ATLAS OWASP HIGH Significant risk · Prioritise patching ▲ 8.2 Dark Reading

New research dubbed 'GhostJacking' demonstrates how attackers can exploit security alerts and blocked events to manipulate and hijack AI agents, exposing fundamental identity governance gaps in agentic AI systems. The technique highlights how defensive signals—normally indicators of protection—can be weaponised to subvert agent behaviour and assume control of automated workflows. This finding has significant implications for enterprises deploying AI agents in sensitive or privileged operational contexts.

Varonis Launches Agent IBAC to Constrain AI Agent Actions at Runtime

Varonis Launches Agent IBAC to Constrain AI Agent Actions at Runtime

FIRST LOOK ATLAS OWASP MEDIUM Moderate risk · Monitor closely ▲ 7.2 BleepingComputer

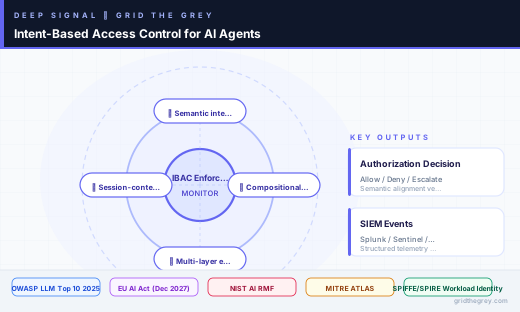
Varonis has released Agent Intent-Based Access Control (IBAC) within its Atlas platform, a runtime enforcement layer that compares an AI agent's received instructions against its actual tool calls and data access to detect and block out-of-policy behaviour. While the capability is a defensive control, its deployment introduces new attack surface: adversaries who understand the intent-matching logic may craft prompt injections or instruction manipulation that causes the agent's declared intent to align with a malicious action, bypassing the guardrail. Security teams should treat Agent IBAC as a layer within a defence-in-depth strategy rather than a standalone control, and test it aggressively against adversarial prompt scenarios before trusting it in production.

AI Agent Security Shifts From Visibility to Enforcement Controls

AI Agent Security Shifts From Visibility to Enforcement Controls

FIRST LOOK ATLAS OWASP HIGH Significant risk · Prioritise patching ▲ 7.8 The Hacker News

Security practitioners are documenting a critical maturity gap in AI agent governance: organisations can now inventory deployed agents across SaaS, cloud, and developer environments, but lack enforcement mechanisms to constrain what those agents can actually do. The core risk is that AI agents operate without consistent identity, intent, ownership, or access boundaries, breaking every assumption that traditional IAM and least-privilege models rely on. Defenders must treat agent enforcement — not discovery — as the primary control objective, or risk a false sense of security from visibility tooling alone.

Anthropic and OpenAI Open Vetted Cyber Programs for Offensive Researchers

Anthropic and OpenAI Open Vetted Cyber Programs for Offensive Researchers

FIRST LOOK ATLAS OWASP HIGH Significant risk · Prioritise patching ▲ 7.2 TechCrunch AI

Anthropic and OpenAI have introduced structured vetting programs — Anthropic's Cyber Verification Program and OpenAI's Trusted Access for Cyber — that grant approved offensive security researchers access to AI models with reduced cybersecurity guardrails. These programs create a two-tier access model where the boundary between legitimate researcher and malicious actor becomes a policy decision made by private companies, introducing new social-engineering and access-abuse vectors. Defenders must now account for the possibility that guardrail-reduced model access can be obtained through credential abuse, insider compromise, or vetting-process manipulation.

IGA Platforms Add AI Agent Governance and Access Control

IGA Platforms Add AI Agent Governance and Access Control

FIRST LOOK ATLAS OWASP HIGH Significant risk · Prioritise patching ▲ 7.8 The Hacker News

A new analysis published via The Hacker News details how traditional Identity Governance and Administration (IGA) frameworks — built around HR-driven, human-centric lifecycle events — are fundamentally unequipped to govern AI agents acting as autonomous principals in enterprise environments. Security teams face a growing blind spot: AI agents acquire, retain, and exercise entitlements without triggering the joiner-mover-leaver workflows, manager attestations, or termination events that IGA tooling depends on. Defenders must now treat AI agent identities as a separate governance tier, requiring purpose-built provisioning, audit, and deprovisioning logic that existing platforms like Workday, SailPoint, and Azure AD connectors were never designed to provide.

◉ AI THREAT BRIEFING

Stay ahead of the threat.

Twice-weekly digest of critical AI security developments — every story mapped to MITRE ATLAS and OWASP LLM Top 10. Free.

No spam. Unsubscribe anytime.