LIVE FEED
Scanning for AI Models, (Tue, Apr 14th)

Scanning for AI Models, (Tue, Apr 14th)

ATLAS OWASP HIGH Significant risk · Prioritise patching ▲ 7.8 SANS Internet Storm Center

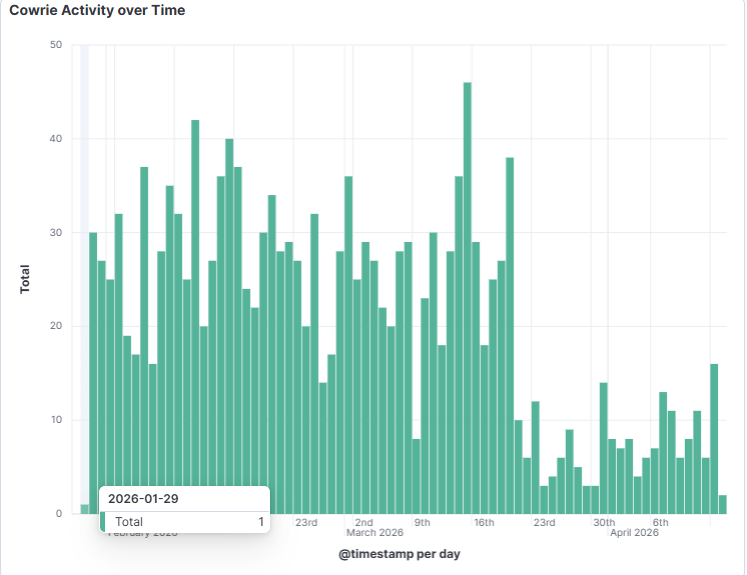
A single threat actor (IP 81.168.83.103) has been systematically scanning internet-facing systems since at least January 2026, specifically targeting credential files, API tokens, and configuration data associated with popular AI platforms including OpenAI, Anthropic Claude, HuggingFace, and the Openclaw/Clawdbot tools. The campaign focuses on harvesting AI API credentials and secrets stored in predictable file paths, representing a targeted reconnaissance effort against AI model deployments. If successful, these probes could enable API key theft, model access abuse, and broader compromise of AI-integrated systems.

OpenAI Supply Chain Attack via Axios Code Signing

OpenAI Supply Chain Attack via Axios Code Signing

ATLAS OWASP HIGH Significant risk · Prioritise patching ▲ 7.5 SecurityWeek

OpenAI has been impacted by a supply chain attack attributed to North Korea-linked threat actors, involving a compromised macOS code signing certificate associated with the Axios JavaScript library. The incident highlights the vulnerability of major AI platforms to upstream software supply chain compromises, which could expose users to malicious code distributed through trusted tooling. As a leading AI infrastructure provider, any compromise of OpenAI's build or distribution pipeline carries significant downstream risk for enterprises relying on its models and APIs.

◉ AI THREAT BRIEFING

Stay ahead of the threat.

Twice-weekly digest of critical AI security developments — every story mapped to MITRE ATLAS and OWASP LLM Top 10. Free.

No spam. Unsubscribe anytime.